Threat Detection Policies
Threat Detection Runtime Policies provide granular control over runtime behavior by defining rules and configurations. Policies specify where to apply rules and how to respond to security violations. Use policies to monitor clusters, hosts, or user-defined tags and take actions. For example, alert Slack channels, trigger webhooks, or prevent malware from executing.
Review the Runtime Policies List
To review the Runtimes Policies list:
Log in to Sysdig Secure.
Select Policies > Runtime Policies.
Here you can see the default policies loaded into Sysdig Secure, as well as any custom policies you have created.
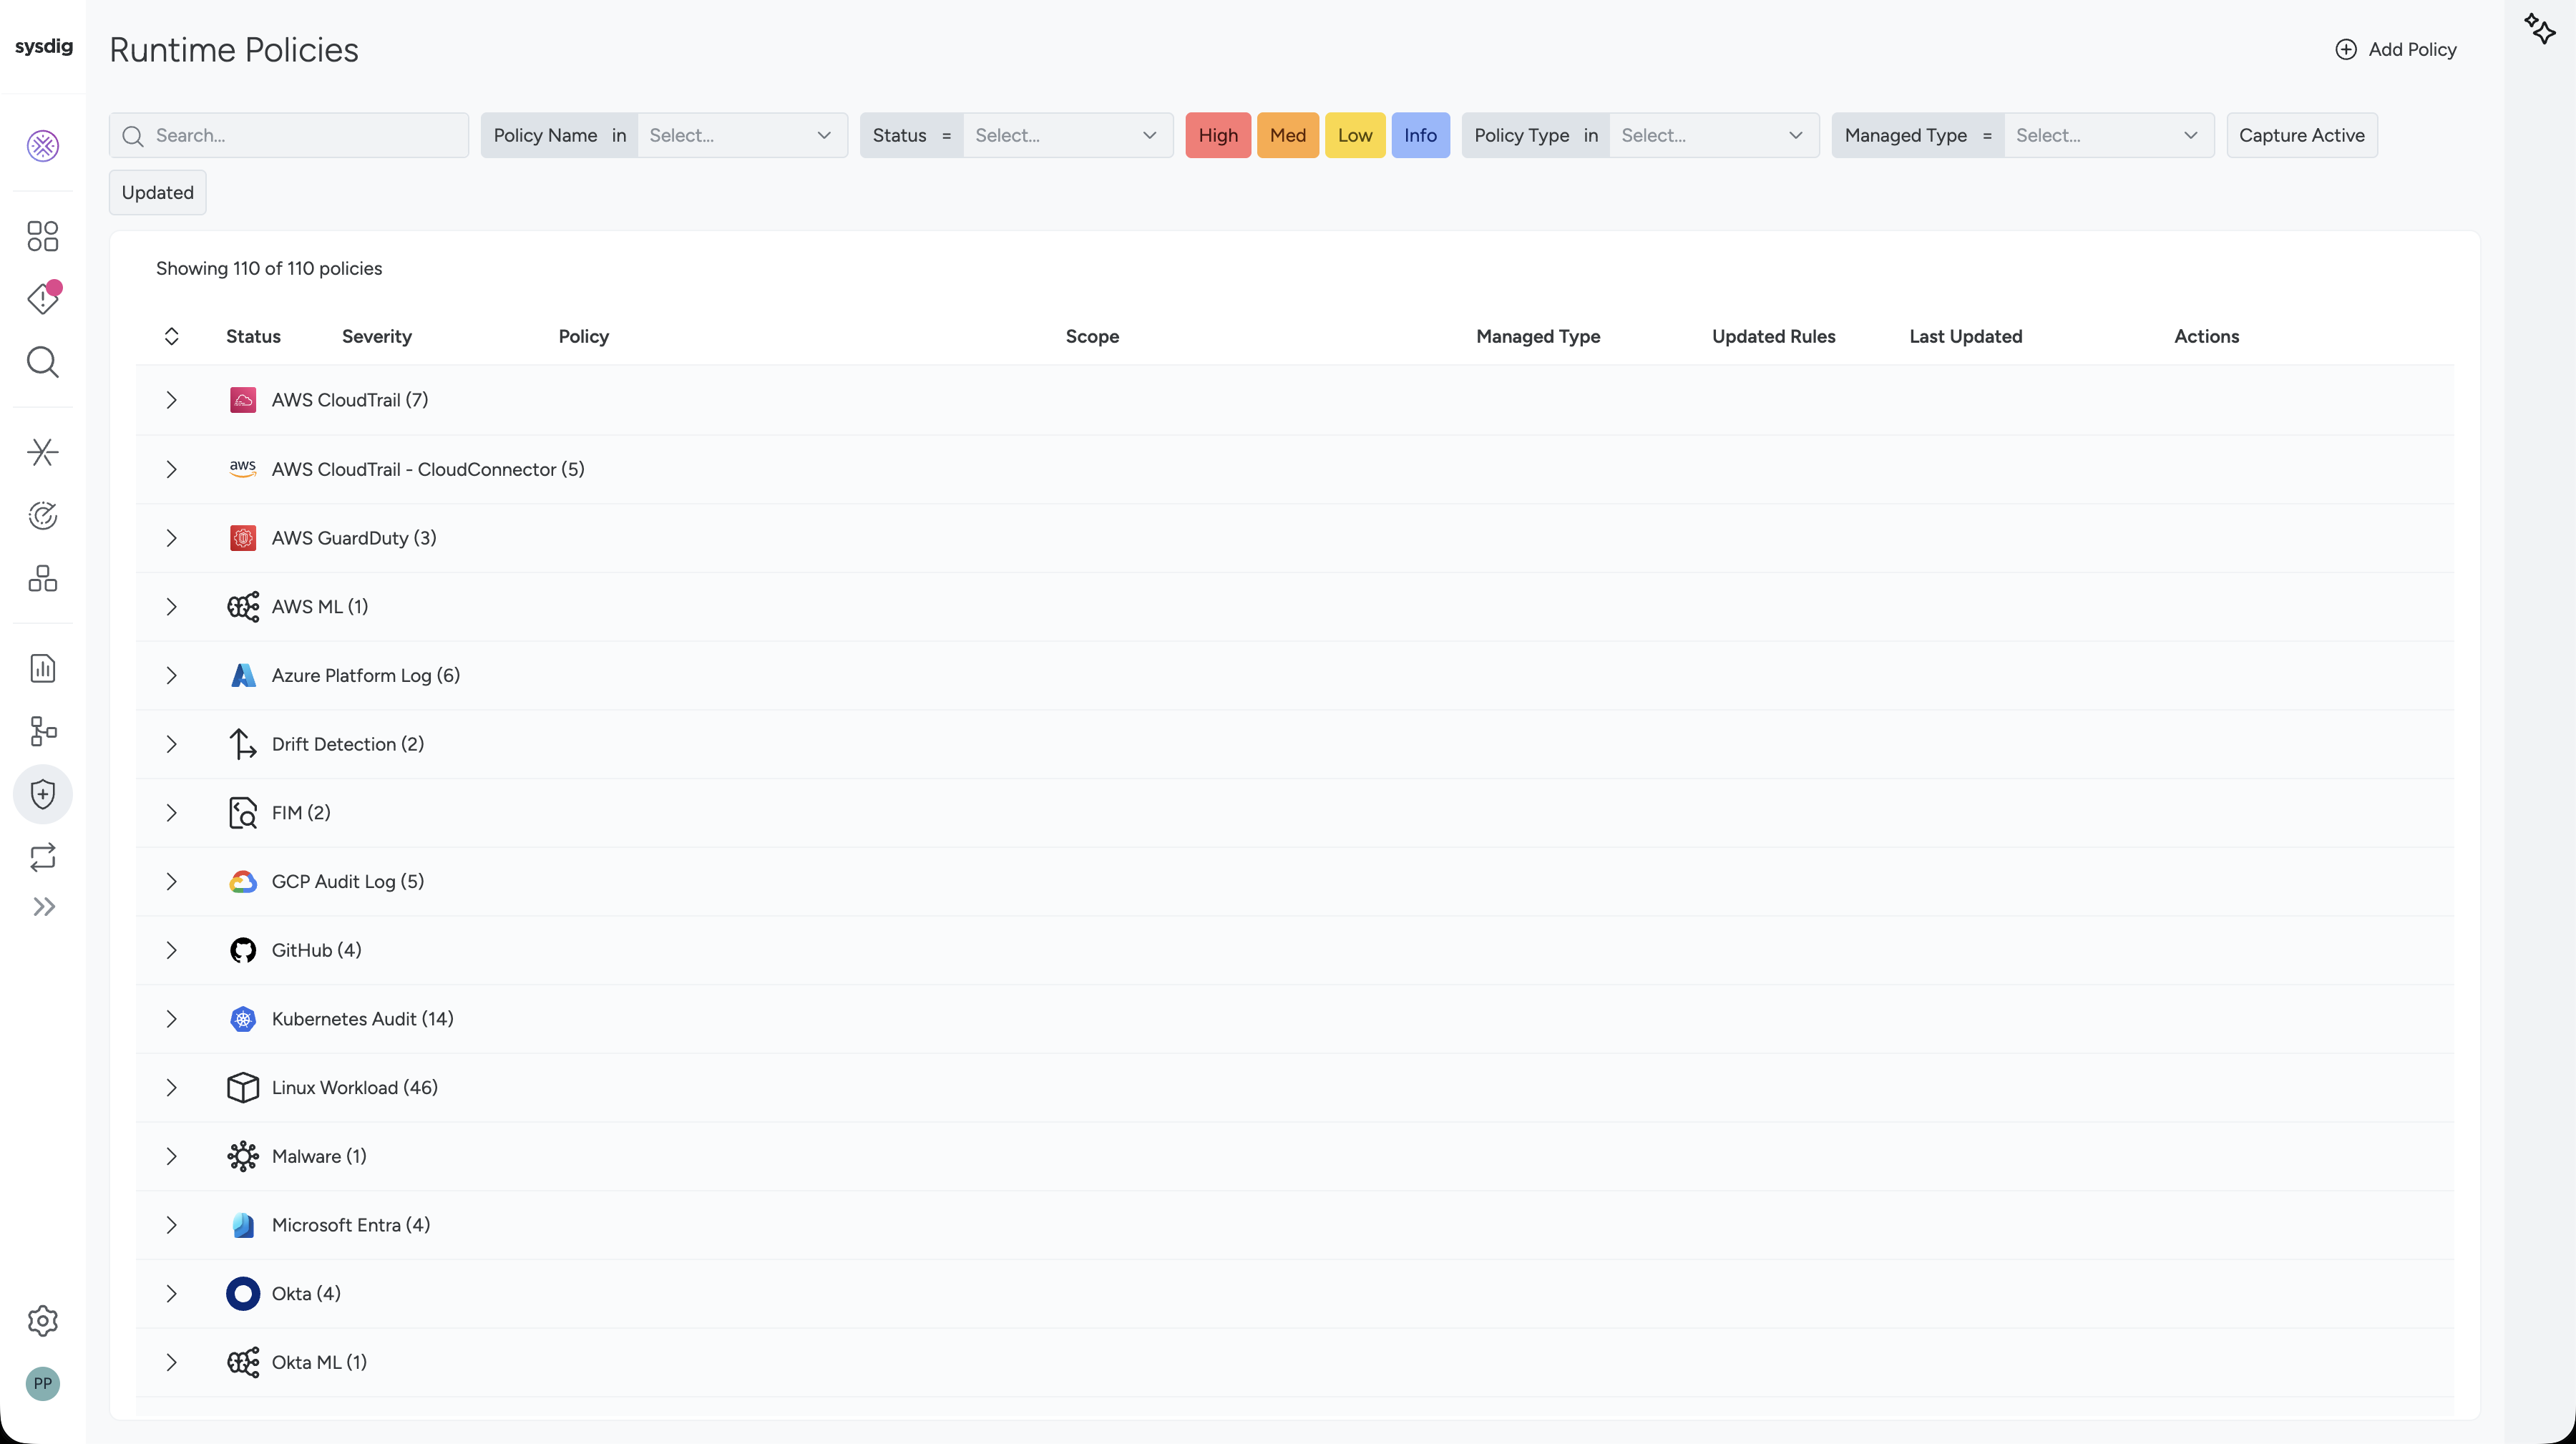
See at a Glance
Policies are grouped by policy type. Collapse or expand a group to show or hide its policies. For each policy, the list shows:
- Status: Whether the policy is enabled or disabled, viewed by toggle position.
- Severity: High, Medium, Low, or Info, which can be edited. See Severity in the API.
- Policy: The policy name and summary, which includes the number of rules, the actions to take on affected containers (Stop | Pause | Notify), and the Capture details, if any.
- Scope: Where the policy applies.
- Managed Type: Managed Policy, Managed Ruleset, or Custom Policy. Custom policies may be designed from scratch or converted from managed policies with changes to their rules. See Manage Threat Detection Policies for details.
- Updated Rules: Whether rules of the policy were updated recently.
- Last Updated: When the policy was last updated.
- Actions: The actions available for the policy.
Take Action
From this page, you can also:
Select a policy to open the details panel, where you can review policy details, and potentially Edit them.
Search and Filter policies by name, status, severity level, policy type, managed type, whether captures are active, or whether they have updates.
Enable or Disable a policy using the toggle.
Create a new policy by selecting +Add Policy.
Policy Types
Threat Detection Policies evaluate different sources. For what each type needs, produces, and supports, see Available Policy Types:
- Workloads: Linux Workload, Windows Workload, Drift Detection, Malware, FIM, and Workload ML
- Kubernetes: Kubernetes Audit
- Cloud and identity: AWS CloudTrail, AWS CloudTrail - CloudConnector, AWS GuardDuty, GCP Audit Log, Azure Platform Log, Microsoft Entra, Okta, GitHub, AWS ML, and Okta ML
Configure Policies
To learn about managed and custom policies, scope, policy actions, notification channels, and how to view recent changes to the rules of a policy, see Manage Threat Detection Policies.
- Managed and Custom Policies
- Policy Actions, including reporting actions in Kubernetes events
- Notification Channels
- View Recent Changes
Getting Started
- Manage Policies
- There are optional tools to help automate the creation of policies. See Network Security Policy Tool for information on authoring and fine-tuning Kubernetes network policies.
- Manage Rules
- Rules are the building blocks of policies. To learn about Falco rules, macros, lists, and the fields you can use, see Manage Threat Detection Rules.
Severity in the API
When you create a policy in the UI, you define the severity as Info, Low, Medium, or High. From an API perspective these are mapped to a number from 0 to 7. When an event is triggered, the corresponding number to the severity is displayed:
| Number | Severity |
|---|---|
| 0 | High (UI Default) |
| 1 | High |
| 2 | High |
| 3 | High |
| 4 | Medium (UI Default) |
| 5 | Low (UI Default) |
| 6 | Info |
| 7 | Info (UI Default) |
